SOC and SIEM in Namibia: What They Are and Whether You Need Them
Most Namibian organisations that suffer a breach find out weeks after it started, usually because somebody else tells them. That interval is where the damage happens, and closing it is what SOC and SIEM services exist to do.
The terms, without the jargon
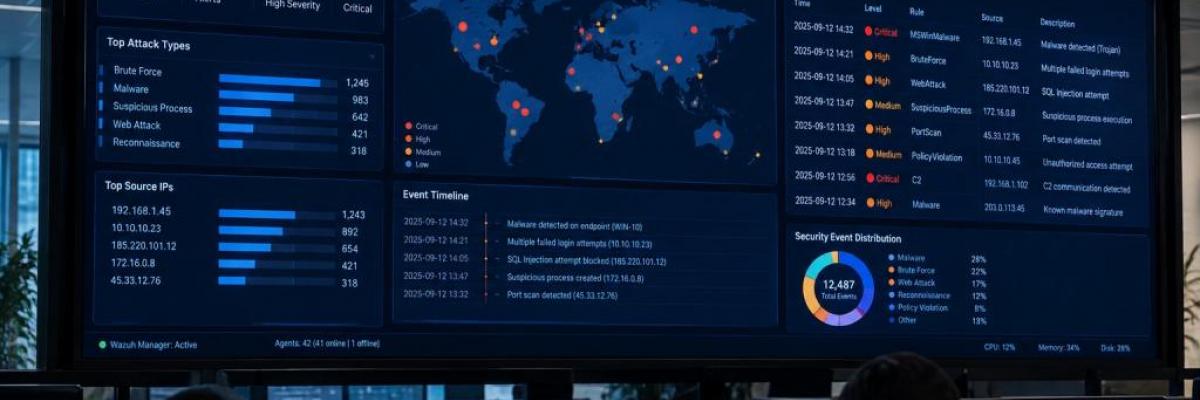
A SIEM, or Security Information and Event Management platform, collects log data from across your environment: servers, firewalls, endpoints, applications, Active Directory, Microsoft 365 and cloud accounts. It normalises that data, correlates it, and raises alerts when patterns look wrong.
A SOC, or Security Operations Centre, is the team and the process that watches those alerts and acts on them.
XDR, or Extended Detection and Response, extends detection and active response across endpoints, network, identity and cloud, so that instead of learning a file was malicious you see which user opened it, what it spawned, what it connected to and which machines it reached afterwards.
The distinction that matters: a SIEM is a tool, a SOC is a function. Buying the first without staffing the second is the most common and most expensive mistake in this market.
Why most Namibian organisations cannot build their own
The arithmetic is unforgiving. Continuous 24-hour coverage requires a minimum of five to six trained analysts to staff a roster, in a country where experienced security engineers are scarce, expensive and heavily recruited abroad. Add platform licensing priced per gigabyte in United States dollars and the total sits beyond almost every Namibian IT budget.
The predictable result is under-logging. Organisations deliberately collect less data than they need because they cannot afford to ingest it, which creates a blind spot on purpose.
What good monitoring actually delivers
Detection of intrusions that do not break anything, which is the category most Namibian organisations currently cannot see at all. Alerts that have been triaged by a human before they reach you. Retained logs that make a forensic investigation possible after an incident. Documentation aligned to the National Cybersecurity Incident Management Guidelines 2026 and to NAM-CSIRT reporting. And evidence your board and auditors can act on.
The Namibian option
Vanguard by Tech49Originals is a Namibian-developed security operations platform combining SIEM correlation, XDR detection and response and network intrusion analysis in a single system. It is built around Namibian bandwidth, priced for Namibian budgets, designed with local data residency in mind and supported from Windhoek.
It is available three ways. Fully managed, with Tech49Originals analysts monitoring and responding on your behalf. Co-managed, where your IT team works in the platform and we cover after hours and escalation. Or platform only, run by your own staff with our onboarding and tuning support.
Do you need it?
If you hold customer data, process payments, operate infrastructure others depend on, or have staff working remotely, then yes. Given that NAM-CSIRT recorded 161,547 cyber events across Namibia in a single quarter of 2026, the relevant question is not whether you will be probed. It is whether anyone is watching when it happens.
Explore Tech49Originals cybersecurity services or contact [email protected] | +264 81 806 8136.